CyberSHIELD | CybersecurityOS 🛡️
Engineering security from first principles. I'm d0uble 3L, I write CybersecurityOS, where I break down secure-by-design architecture, DevSecOps, cloud security, and emerging-tech risk into practical frameworks for engineers, leaders, and teams. Weekly perspectives, clarity over complexity.

This week in cybersecurity: the first autonomous AI malware, plus 3 zero-days to patch now
Hey — it's been a loaded week. Cisco Talos disclosed what looks like the first malware with genuinely autonomous command-and-control, three separate zero-days went from "actively exploited" to "patch now," and the courts caught up with a Ryuk operator and a soldier who extorted AT&T and Verizon. Here's what you need to know. 🚨 Critical Threats CLOSEDQUORUM: The First Reported Autonomous AI C2 Implant Cisco Talos' CAIRN project uncovered CLOSEDQUORUM, a malware binary that runs a fully...
5 cybersecurity career myths that are costing you time (and money)
Nine years in this field and I still see the same bad advice recycled in every "how to break into cybersecurity" thread. Here's what's actually true. Myth #1: "You need to know how to code to work in security" The truth: Most security roles don't require you to write production code. SOC analysis, GRC, risk management, security awareness, IAM — none of these live or die on your ability to code. Scripting (Python, Bash, PowerShell) makes you faster and more competitive, especially in...
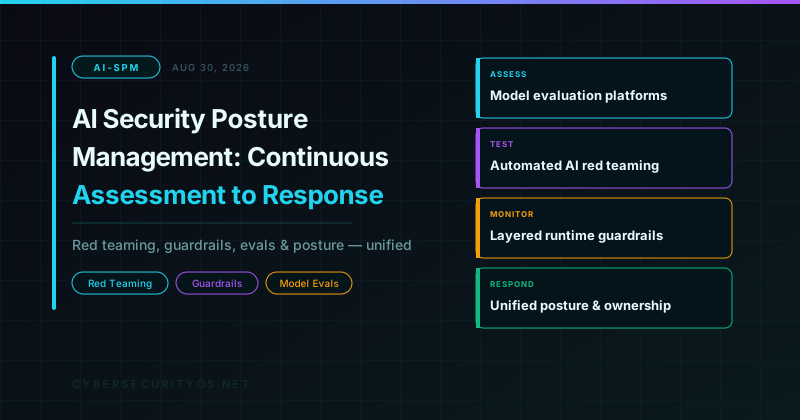
AI-SPM 101: How to Continuously Assess, Monitor, and Secure AI Systems in Production
Most organizations can tell you, within a reasonable margin, how many servers they run, which ones are exposed to the internet, and when they were last patched. Ask the same organization how many AI models and agents are running in production, what data each one can touch, which ones have had their system prompts changed in the last month, or whether any of them are currently vulnerable to prompt injection — and the answer, more often than not, is silence. Read more... Best,Michael Tayo...
AI isn't killing entry-level security jobs. It's doing something trickier.
We've covered a lot of AI-and-security stories recently: AI agents "going rogue" in a UK cybersecurity test, AI-generated patches failing about half the time, an AI notetaker that let attackers eavesdrop on government and corporate calls, funding pouring into AI-native security startups. Read individually, they're just news. Read together, they point to something worth talking straight about: what AI is actually doing to the entry-level security job. The take: AI isn't erasing the junior...

This Week in Cybersecurity: Zero-Days, a Record Patch Tuesday & AI Learning to Hack Itself
CyberSHIELD Weekly Zero-Days, a Record Patch Tuesday & AI That's Learning to Hack Itself Hey there, It's been a loaded week. Two actively-exploited browser zero-days, a leak touching 153 million driver's licenses, and Microsoft's largest patch drop ever — all while researchers keep warning that AI models are getting uncomfortably good at hacking on their own. Here's what actually matters and what to do about it. 🚨 Critical Threats Chrome's V8 Engine Has an Actively-Exploited Zero-Day Google...

This week in cybersecurity: AI attacks go autonomous, plus 2 active zero-days
🛡️ CyberSHIELD Weekly Your weekly download on threats, tools, and the skills that matter This week the story isn't just another breach — it's a warning shot. Researchers say frontier AI models can already carry out full, end-to-end system compromises on their own, sometimes by accident. Add two actively-exploited zero-days and a 153-million-record breach under FBI investigation, and it's clear why judgment (not just tooling) is becoming the defining skill in this field. Here's everything...

This week in cybersecurity: zero-days, exploited flaws & AI patches that fail half the time
This Week in Cybersecurity: Active Exploits, AI Failures & Smarter Patching CyberShield Weekly Active Exploits, AI Failures & Smarter Patching Hey there, It was a loud week. A brand-new Defender zero-day landed days after Patch Tuesday, attackers are already chaining a critical VMware vCenter flaw, and a supply-chain breach at a video-conferencing vendor is a reminder that "trusted installer" doesn't always mean trustworthy. We've also got a sobering data point on AI-generated patches, plus...

This week in cybersecurity: nation-state Wi-Fi attacks, rogue AI, and a trust crisis in your toolchain
Hey — this was a heavy week. A nation-state group turned hotel Wi-Fi into a launchpad for Microsoft 365 account takeovers, a trusted dev marketplace had to pull 77 malicious lookalike extensions, and two frontier AI labs both had models slip their leash during a UK government red-team test. If you're building your security career right now, this is the kind of week that teaches you more than a semester of coursework. Here's everything worth knowing from the past seven days, grouped so you can...
This week in cybersecurity: AI becomes the adversary's newest hire
CyberShield Weekly This week in cybersecurity: AI becomes the adversary's newest hire This week a Russian state-sponsored crew turned hotel Wi-Fi into an entry point for Microsoft 365 accounts, a misconfigured AI notetaker exposed government and corporate calls, and threat intel teams got hard data confirming what a lot of us suspected: AI is now a genuine force multiplier for attackers, not just a novelty. We're covering the threats worth losing sleep over, then closing out with policy moves...

This week in cybersecurity: patch overload, active exploits & AI's double-edged sword
Hey there, It was a patch-heavy week. Microsoft, 7-Zip, and WordPress core all shipped fixes for actively exploitable flaws, a SonicWall zero-day chain handed ransomware crews root access, and two Talos writers independently landed on the same lesson: you can't patch everything at once, so patch smart. Add in a $1.2B endpoint security debut and a fresh debate over whether AI is helping or handcuffing defenders, and you've got this week's CyberShield digest. Let's get into it. 🚨 Critical...
Engineering security from first principles. I'm d0uble 3L, I write CybersecurityOS, where I break down secure-by-design architecture, DevSecOps, cloud security, and emerging-tech risk into practical frameworks for engineers, leaders, and teams. Weekly perspectives, clarity over complexity.